Author: Shao Jiadan
Recently, Ledger has become embroiled in an asset loss incident. Some Southeast Asian users reported that after purchasing hardware wallets from the reseller CryptoBilis, the assets in their wallets were transferred away. On October 9, Ledger announced that it had launched an investigation, asked this reseller to suspend sales and shipments, and reminded recent buyers to hold off on setting up their devices, while users who had already set them up should consider migrating their assets.
On October 10, Ledger further stated that an unauthorized hardware implant had been found in the device of one affected user. The company said at the time that it had confirmed the cases were related to devices sold by this reseller, and that no signs had been found of intrusion into its security infrastructure, systems, or services.
According to Bitquery's statistics, the related asset outflows involved 315 wallets and approximately $93.2 million. This is a third-party statistic, and Ledger has not yet confirmed the final scale of the losses. As of October 12, it is still under investigation at which stage the devices were tampered with, and whether the implant is related to all the losses.
Many people choose hardware wallets precisely because they hope to keep their assets more securely. Now that user-reported losses and anomalies on the devices have appeared at the same time, it is inevitably worrying. Determining the cause of the attack requires professional testing, and as for whether this discovery can explain all the losses, there is not yet a complete conclusion. For other wallet teams, this incident has already raised a question worth discussing: when users trust a wallet, which links in the chain are they actually trusting?
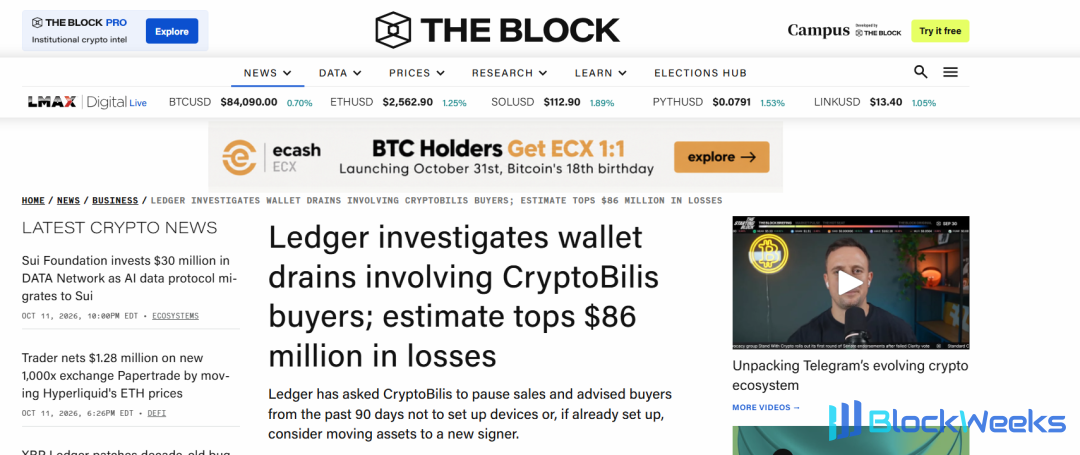
Image source: The Block, report dated October 9, 2026. The amount in the screenshot is an early estimate, and the scale of the losses is still under verification.
What makes this incident unsettling is that CryptoBilis had previously been on Ledger's official authorized reseller list. Users who went to the official website to check the list and buy through authorized channels were already carefully avoiding risk. Now, this purchasing path has also entered the scope of the investigation. For other hardware wallets and non-custodial wallet apps, what is worth discussing is: when users place their trust in a brand, are the commitments made and responsibilities borne by the manufacturer stated clearly enough?
01 | The trust brought by "official authorization" is something brands need to take seriously
It is very difficult for ordinary users to know what a device has gone through after leaving the factory. When they choose an authorized reseller, they usually believe that the brand has already screened the channel. Therefore, when a reseller has a problem, users will naturally also seek explanations and help from the brand.
For example, a user worried about buying a counterfeit product specifically checked the reseller list on the brand's official website, and then placed an order with a shop on that list. The reason this shop gained his trust involved both factors related to the shop itself and the role of the brand's recommendation. If the device later had a problem, it would be hard for him to accept the brand and the seller telling him to "go find the other party." This is an understandable user reaction, while legal liability still needs further clarification.
Brands and resellers are often two different business entities, and users usually cannot see the contracts between them or the division of after-sales responsibilities. If what authorization includes, which stages the brand participated in, and what help is provided after an anomaly occurs are stated vaguely to the outside, it is easy for a gap to appear between users' expectations and the actual arrangements of both parties.
Users may not necessarily care how the brand and reseller manage and cooperate with each other, but these arrangements will affect how things are handled after an incident occurs. How much management authority the brand has over the channel, who reports anomalies, who contacts users, and who is responsible for after-sales service should preferably be clearly agreed upon at the time of cooperation.
From a contractual perspective, the value of such agreements lies in reducing disputes after an incident. Whether the reseller can provide purchase records, whether the brand can directly contact the relevant users, and how the two parties cooperate in the investigation will all affect how matters proceed. The specific channel management method to adopt needs to be determined in light of the judgment of the business and security teams; at the very least, both parties should know what they have promised and what they need to cooperate on if a problem arises.
Whether the brand bears responsibility and how much it bears depends on what problem occurred with the device, what commitments each party made, and the connection between the relevant conduct and the losses. But since "official authorization" participated in users' purchasing decisions, the brand needs to take seriously the trust arising from it.
For other hardware wallet manufacturers, authorized relationships are worth reexamining. When the official website recommends a certain channel, how will users understand this recommendation? If changes occur during the cooperation period, can the original arrangements still function? These questions are related to how the brand uses the words "official authorization," and also to whom users assert their rights after losses occur.
02 | However great the security capability, the commitments should go only that far
Ledger's security research team Donjon explained in public materials that Genuine Check mainly verifies the authenticity of the secure chip. As long as the original secure chip remains intact, some additional hardware modifications may not be identified. This check also cannot verify the device's complete sales and delivery history.
For users, "verification passed" is easily understood as "the device is safe and can be used with confidence." If the scope actually checked by the product is narrower, it is necessary to explain this difference clearly. Whether security notices are understandable to ordinary users is also part of the product commitment.
The difficulty here is that technical teams and ordinary users may understand the same sentence differently. Technical personnel know which component a check verifies, while what users see may be only a green mark. The check itself has completed its assigned task, but users may still overestimate the protection it provides. Product descriptions need to take this difference in understanding into account.
If the purchase page repeatedly emphasizes security while key limitations are placed only in instructions that are very hard for users to find, then two positions may emerge in a dispute: the manufacturer believes it has already explained, while users believe they were never reminded when purchasing and using the product. Whether this constitutes misleading and whether the notices are sufficient requires looking at the specific pages and applicable law. But explaining the limitations more clearly can indeed help reduce such disagreements.
Non-custodial wallet apps have similar issues. "Open-source code," "audited," and "private keys are kept by users" each explain a certain feature of the product. Users may form broader security expectations based on them. When manufacturers promote their products, accurately explaining the scope of these capabilities helps reduce misunderstandings and can also reduce future disputes over liability.
For example, a certain app describes itself as having undergone a security audit. Users may understand this sentence to mean that future use will all be safe, whereas an audit usually has a corresponding object, version, and scope. Accurately explaining this information does not weaken the capabilities the product already has. It gives users an opportunity to understand which claims a particular audit report specifically supports.
Of course, it is very difficult for wallet manufacturers to guarantee that all risks will disappear. What we care about more is whether external commitments match actual capabilities, and whether important limitations are made known to users. The greater the gap among promotion, security descriptions, and user agreements, the easier it is, after an incident, for disputes to arise over "what exactly was promised at the time."

Image source: Ledger Donjon official website, screenshot dated October 12, 2026. The page explains the limitations of Genuine Check in detecting additional hardware modifications.
03 | Private keys are kept by users, but products and services still have their respective responsibilities
In non-custodial wallets, users usually hold the private keys or signing authority. Users need to safeguard recovery information and carefully verify transactions. But users still rely on manufacturers to provide devices, software, and page information. If problems occur in these links, "we do not custody private keys" does not answer the cause of the incident or the attribution of responsibility.
When users use a non-custodial wallet, they may be responsible for signing themselves, but the transaction content they see, the swap entry points they use, and the software updates they receive still come from the wallet and its partners. There are different participants here, and also different tasks. The fact that assets are controlled by users does not make these service relationships disappear.
For example, a user uses a third-party swap service in a wallet and later discovers that a problem occurred with the transaction. The user needs to know who provides the service, up to which step the wallet is involved, and at which link the problem occurred. The wallet may merely display the entry point, or it may have participated in generating and displaying the transaction content; different situations will have different impacts on the determination of responsibility. The brand marks on the page and the "third-party services" in the contract both need to be viewed in the context of the actual process.
From a lawyer's perspective, product commitments, risk disclosures, cooperation contracts, and user agreements are important materials for discussing these issues. They can help reconstruct what each party agreed to, but they still need to be compared with the products and services actually delivered. A general "non-custodial" label can hardly explain all the relationships.
There will be differences in determining responsibility between a user leaking their mnemonic phrase and losses caused by device defects, software vulnerabilities, or misleading promotion. User agreements can stipulate the responsibilities of each party, but the effectiveness of exemption clauses still depends on applicable law and specific circumstances. Regarding this Ledger incident, it is still necessary to wait for the investigation to complete the facts before discussing compensation.
Communication after an incident also affects whether users can continue to trust the product. While an investigation is still ongoing, manufacturers can explain the facts currently known, the issues being addressed, and where users can get help. For matters that have not yet been determined, leaving necessary room is more prudent than hastily assuring that there is "no problem."
Suspending a certain channel, assisting with an investigation, or providing replacement devices are all concrete measures in incident handling. Liability for compensation still needs to be judged based on the investigation results and the agreements of the parties involved. Whether assets can be successfully recovered also involves where the funds went and the authority of the relevant institutions. Users need to know what support is currently available and how they can subsequently handle their own claims.
Mankun Lawyer Summary
The technical cause of the Ledger incident remains to be determined by a professional team. As lawyers, we are more concerned with the relationship between user trust and the commitments of the parties involved: whether the authorization on the official website, the security statements on the pages, and the liability arrangements in the agreements can correspond to the products and services users actually receive.
Other wallet teams can re-examine their own business from this perspective. Users holding their own assets need to bear the corresponding custody responsibilities; what manufacturers provide and promise is also worth explaining clearly. A relatively consistent understanding among all parties on these matters helps reduce misunderstandings in ordinary times and makes it easier to discuss what to do next when problems arise.





